Create firewall rules to handle the network traffic according to your requirements.
Click the Trellix menulet
 on the status bar, then select Preferences.
Click Firewall.
Click
 , type the administrator password, then click OK.
Select Regular Mode.
Click
 in the bottom left corner of the console to open the rule page.
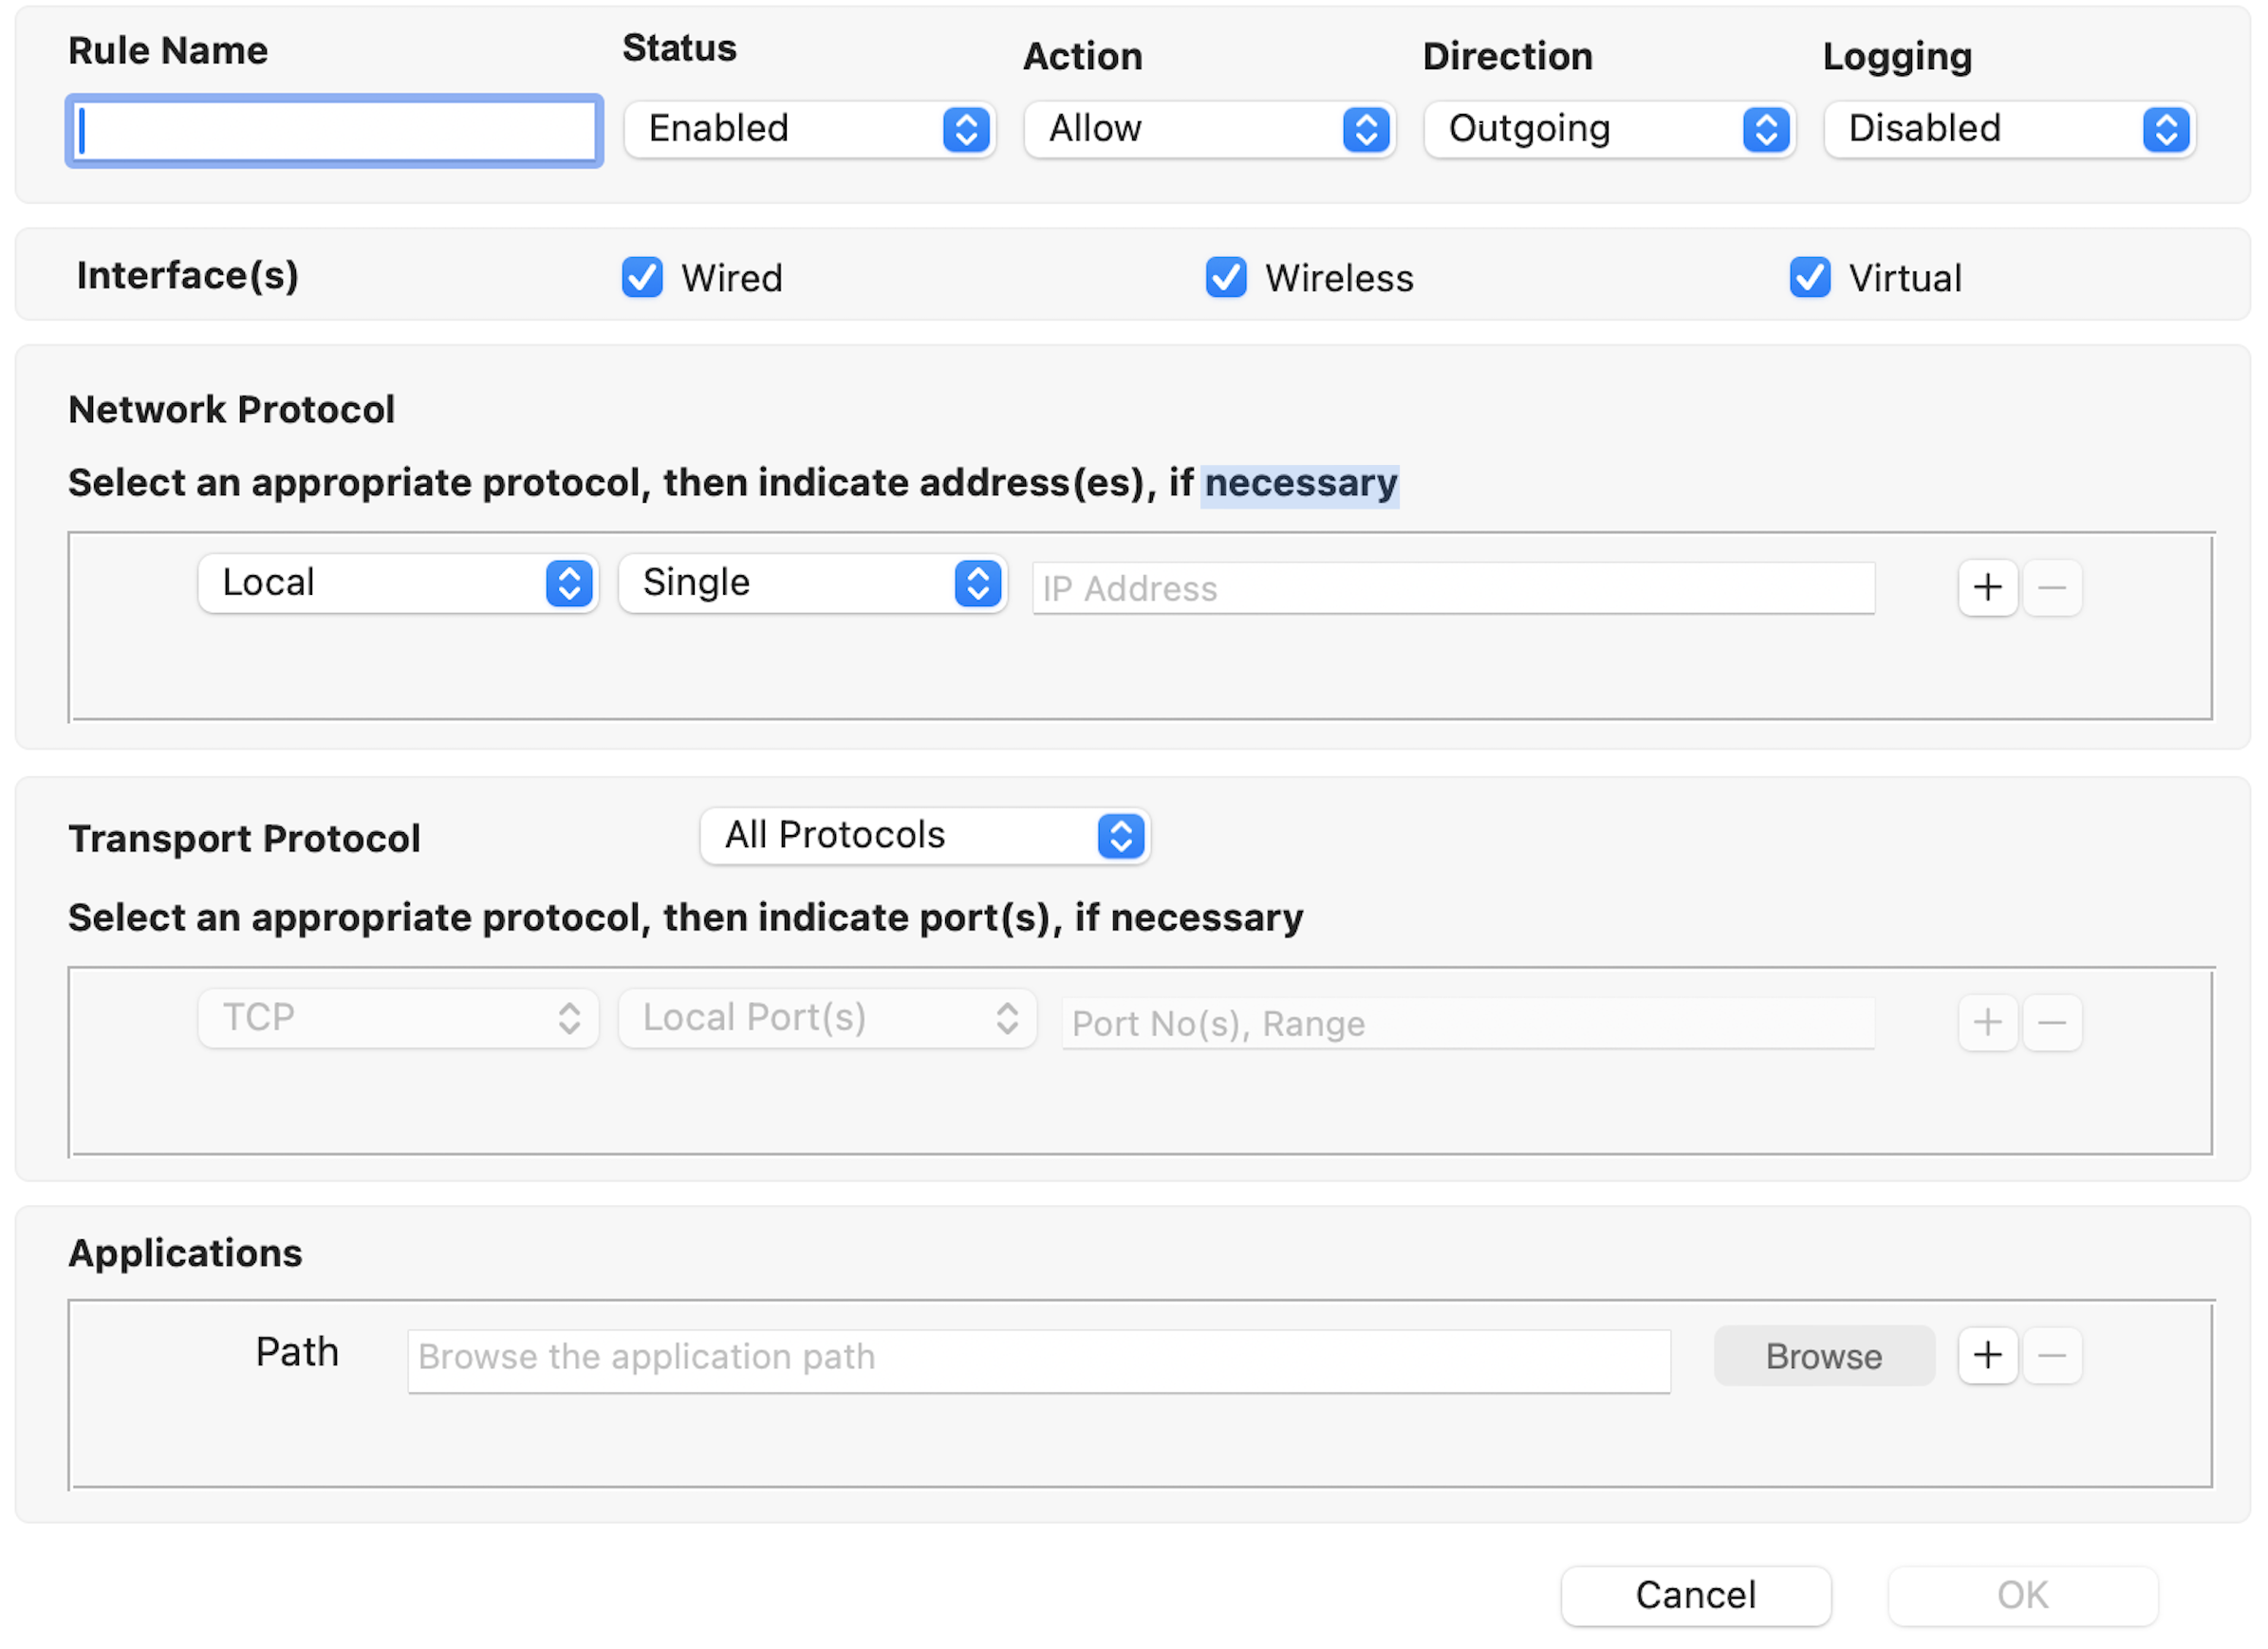
Define the following parameters as needed, then click OK.
For this field...
Configure these options...
Rule Name
Type a name for the rule.
Status
Enabled — To enable the firewall rule.
Disabled — To disable the firewall rule.
Note
The rules appear as grayed out in the rules list, when their status is set to Disabled.
Action
Block — To block the network traffic.
Allow — To allow the network traffic.
Direction
Incoming — To apply the rules for incoming network traffic.
Outgoing — To apply the rules for outgoing network traffic.
Logging
Enabled — To make an entry in the system log, when a network packet matches a rule.
Disabled — To avoid making an entry in the system log when the network packet matches a rule.
Caution
Enabling the logging feature can impact the system performance. We recommend that you enable Logging only for troubleshooting and learning purpose.
Interface(s)
Wired
Wireless
Virtual
Network Protocol
Define the configuration for Local Mac using:
Single
Subnet
Local Subnet
Range (of IP addresses)
Fully Qualified Domain Name
Any local IP Address
Any IPv4 or IPv6 Address
Tip
Local system is the system on which you are adding rules.
Select the configuration for Remote system using:
Single
Subnet
Local Subnet
Range (of IP addresses)
Fully Qualified Domain Name
Any local IP Address
Any IPv4 or IPv6 Address
Tip
Remote system is the system you want to connect.
Note
Use
 to add more criteria and
 to remove existing criteria.
Transport Protocol
Select All Protocols to apply the rule for all protocols.
For Select Protocol, define the parameters for:
TCP
UDP
ICMP
Note
Use
to add more criteria and to remove existing criteria.Tip
Add specific rules at the top of the list, and generic rules at the bottom to filter the traffic most efficiently.
In Applications, click Browse, select the application from the Applications directory, then click Open.
Note
When you select a bundle, the product enumerates through the bundle and lists all Mach-O binaries, that are part of the bundle, in the rule. Wildcards are not supported in the application path and name.
Click
 to prevent further changes.
Note
To edit an existing Firewall rule, select the rule, then click Edit to open the rule page.