Threat Prevention enforces Expert Rules on the client system the same as any other rule.
The signatures in the Exploit Prevention content provide default protection from Trellix Advanced Research Center. If you need to protect additional resources, you can create custom rules in the Access Protection policy. For even further customization, create Expert Rules in the Exploit Prevention policy.
Note
Exploit Prevention is not supported in the ARM architecture.
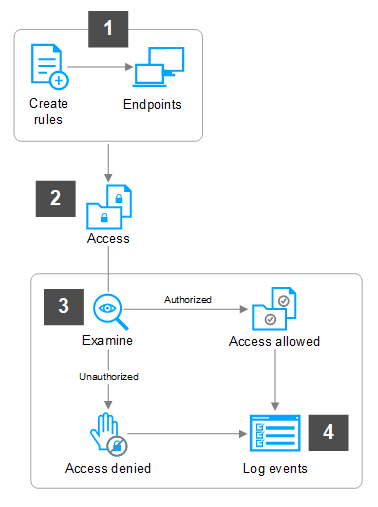
Here is the workflow of Expert rules:
An administrator creates the Expert rules and enforces them on the client system or self-managed endpoints.
A user or application tries to access the specific object on which the Expert rules are enforced.
Rules examine and perform one of these actions:
a) allow access if user identity, access types, and other match values comply with the rule.
b) block access if user identity, access types, and other match values do not comply with the rule.
Log events in the Event Log page of ENS.