Firewall rule groups organize firewall rules for easy management. The software includes predefined rule groups with rules that allow needed services, such as ePO - On-prem and DNS, to run.
Firewall rule groups don't affect the way Firewall handles the rules; the software processes rules from top to bottom.
Firewall processes the settings for the group before processing the settings for the rules it contains. If a conflict exists between these settings, the group settings take precedence.
You can create customized rule groups such as Timed groups which are active for a set time.
You can also create nested groups. The nested groups help in enhancing the efficiency of firewall rule organization. For instance, you can apply protocol settings at the group level, determine the direction at the group level, and schedule a group (also known as timed group) to be active during specific intervals. The subgroups and rules nested beneath it will also be in effect for the same designated period.
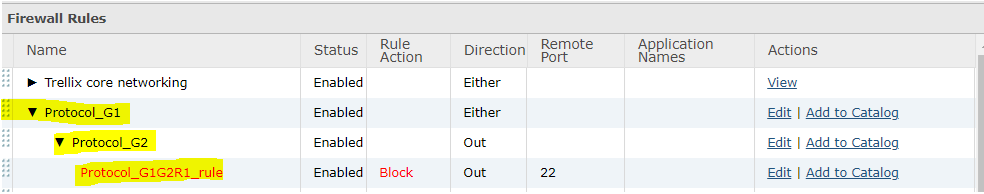
Sample configuration with Nested rules
The group Protocol_G1 has nested group Protocol_G2 and within the group you will find the actual rule Protocol_G1G2R1_rule.
Note
The direction of the groups, subgroups, and rules should match. For instance, If the direction of Protocol_G1 is In, the direction for the nested group Protocol_G2 should also be In. In the conflicting case, Protocol_G2 will not be enforced.