Firewall rules determine how to handle network traffic. Each rule provides a set of conditions that traffic must meet, and an action to allow or block traffic.
When Firewall finds traffic that matches a rule’s conditions, it performs the associated action.
You can define rules broadly (for example, all IP traffic) or narrowly (for example, identifying a specific application or service) and specify options. You can group rules according to a work function, service, or application for easier management. Like rules, you can define rule groups by network, transport, application, schedule, and location options.
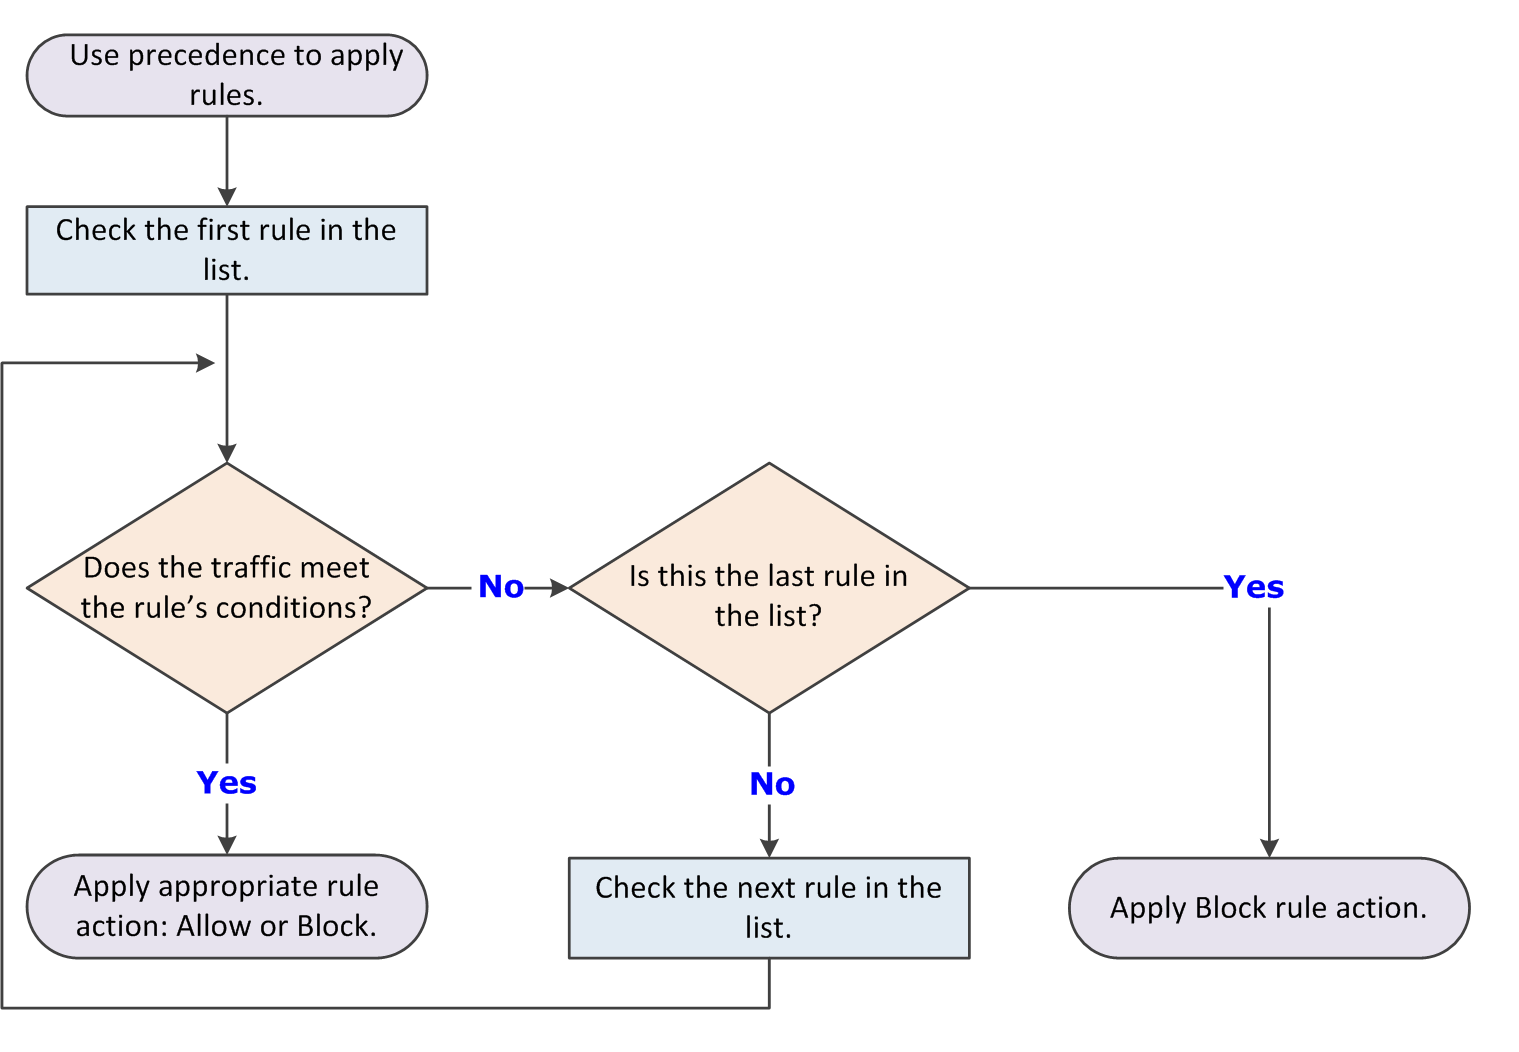
Firewall uses precedence to apply rules:
Firewall applies the rule at the top of the firewall rules list.
If the traffic meets this rule’s conditions, Firewall allows or blocks the traffic. It doesn't try to apply any other rules in the list.
If the traffic doesn't meet the first rule’s conditions, Firewall continues to the next rule in the list until it finds a rule that the traffic matches.
If no rule matches, the firewall automatically blocks the traffic.
If Adaptive mode is activated, an Allow rule is created for the traffic. Sometimes the intercepted traffic matches more than one rule in the list. In this case, precedence means that Firewall applies only the first matching rule in the list.
Best practices
Place the more specific rules at the top of the list, and the more general rules at the bottom. This order makes sure that Firewall filters traffic appropriately.
For example, to allow all HTTP requests except from a specific address (for example, IP address 10.10.10.1), create two rules:
Block rule — Block HTTP traffic from IP address 10.10.10.1. This rule is specific.
Allow rule — Allow all traffic using the HTTP service. This rule is general.
Place the Block rule higher in the firewall rules list than the Allow rule. When the firewall intercepts the HTTP request from address 10.10.10.1, the first matching rule it finds is the one that blocks this traffic through the firewall.
If the general Allow rule is higher than the specific Block rule, Firewall matches requests against the Allow rule before finding the Block rule. It allows the traffic, even though you wanted to block the HTTP request from a specific address.