TIE comprises a module for Endpoint Security that allows you to create policies for blocking and allowing a file based on its reputation. It has a server that stores information about file and certificate reputations, then passes that information to other systems. Finally, it has Trellix DXL brokers that allow bidirectional communication between managed systems on a network.
The module and server exchange file and certificate reputation information. The Trellix DXL framework immediately passes that information to managed endpoints. It also shares information with other Trellix products that access the Trellix DXL, such as Trellix Enterprise Security Manager and Trellix Intrusion Prevention System.
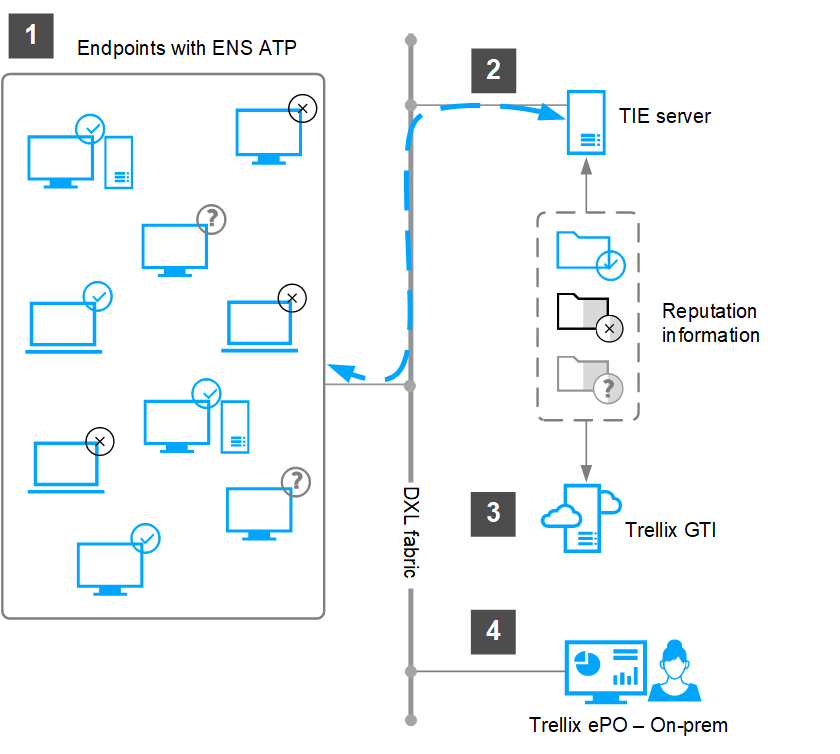
Endpoints running Trellix Endpoint Security Adaptive Threat Protection (ATP) query the TIE server on every executed file in the environment, including unknown files. Files are automatically blocked or allowed based on information stored on TIE and Trellix GTI.
The TIE server analyzes the files and shares threat information throughout the environment based on its security reputation and criteria set by you. In addition to identifying the file's reputation, the TIE server also adds local intelligence capabilities to the ecosystem such as age and prevalence of files.
Integration with Trellix GTI provides a base reputation to the TIE server.
The security administrator can spend time monitoring unusual activity.