Each rule contains a set of conditions that the network traffic must meet. The associated parameters of that rule allow or block the network traffic.
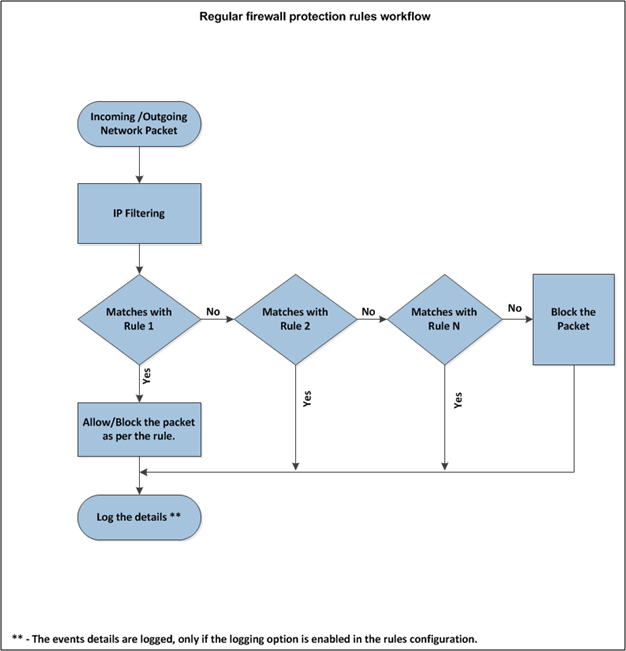
In Regular mode, firewall uses precedence to apply rules. The rule at the top of the rules list is applied first. If the network packet meets the conditions, firewall allows or blocks the packet as defined. If the packet does not meet the first rule's condition, the next rule is verified and moves through the rules list until a rule is satisfied. If no rule is met from the rules list, firewall blocks the traffic.
When the traffic matches the rule condition, firewall does not try to apply any further rules from the list.
Note
To change the firewall protection from Regular mode to Adaptive mode, click
| Preferences | Firewall | Adaptive Mode.