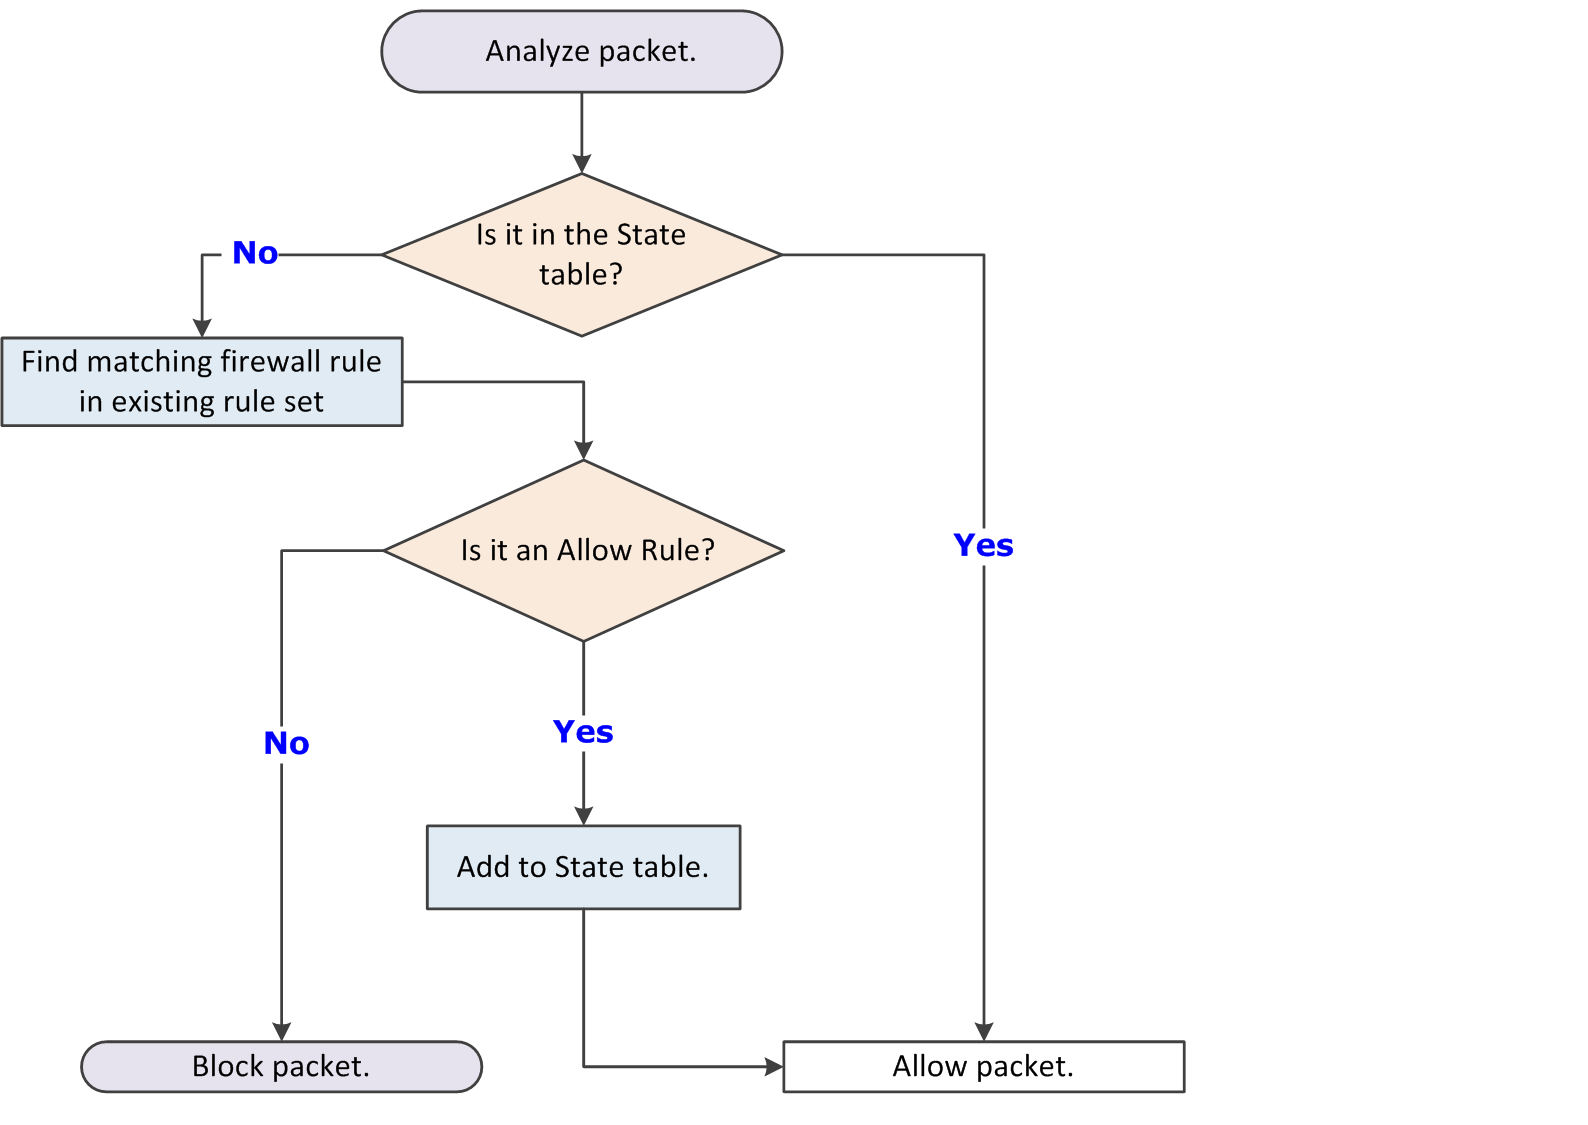
Stateful filtering involves processing a packet against two rule sets: a configurable firewall rule set and a dynamic firewall rule set or state table.
The configurable rules have two possible actions:
Allow — The packet is permitted and an entry is made in the state table.
Block — The packet is blocked and no entry is made in the state table.
The state table entries result from network activity and reflect the state of the network stack. Each rule in the state table has only one action, Allow, so that any packet matched to a rule in the state table is automatically permitted.
The filtering process includes the following:
The firewall compares an incoming packet against entries in the state table. If the packet matches any entry in the table, the packet is immediately allowed. If not, the configurable firewall rules list is examined.
Note
A state table entry is considered a match if the Protocol, Local Address, Local Port, Remote Address, and Remote Port match those elements of the packet.
If the packet matches an Allow rule, it is allowed and an entry is created in the state table.
If the packet matches a Block rule, it is blocked.
If the packet doesn't match any configurable rule, it is blocked.