The Threat Prevention script scanner intercepts and scans scripts before they are executed.
ScriptScan is a Browser Helper Object that examines JavaScript and VBScript code for malicious scripts before they are executed. If the script is clean, it passes to JavaScript or VBScript for handling. If ScriptScan detects a malicious script, it blocks the script from executing.
Note
ScriptScan examines scripts for Internet Explorer only. It doesn't look at scripts system-wide and doesn't examine scripts run by wscript.exe or cscript.exe.
When Threat Prevention is installed, the first time that Internet Explorer starts, a prompt to enable one or more Trellix add-ons appears. For ScriptScan to scan scripts:
The Enable ScriptScan setting must be selected. ScriptScan is enabled by default.
The add-on must be enabled in the browser.
Caution
If ScriptScan is disabled when Internet Explorer starts and then is enabled, it doesn't detect malicious scripts in that instance of Internet Explorer. You must restart Internet Explorer after enabling ScriptScan for it to detect malicious scripts.
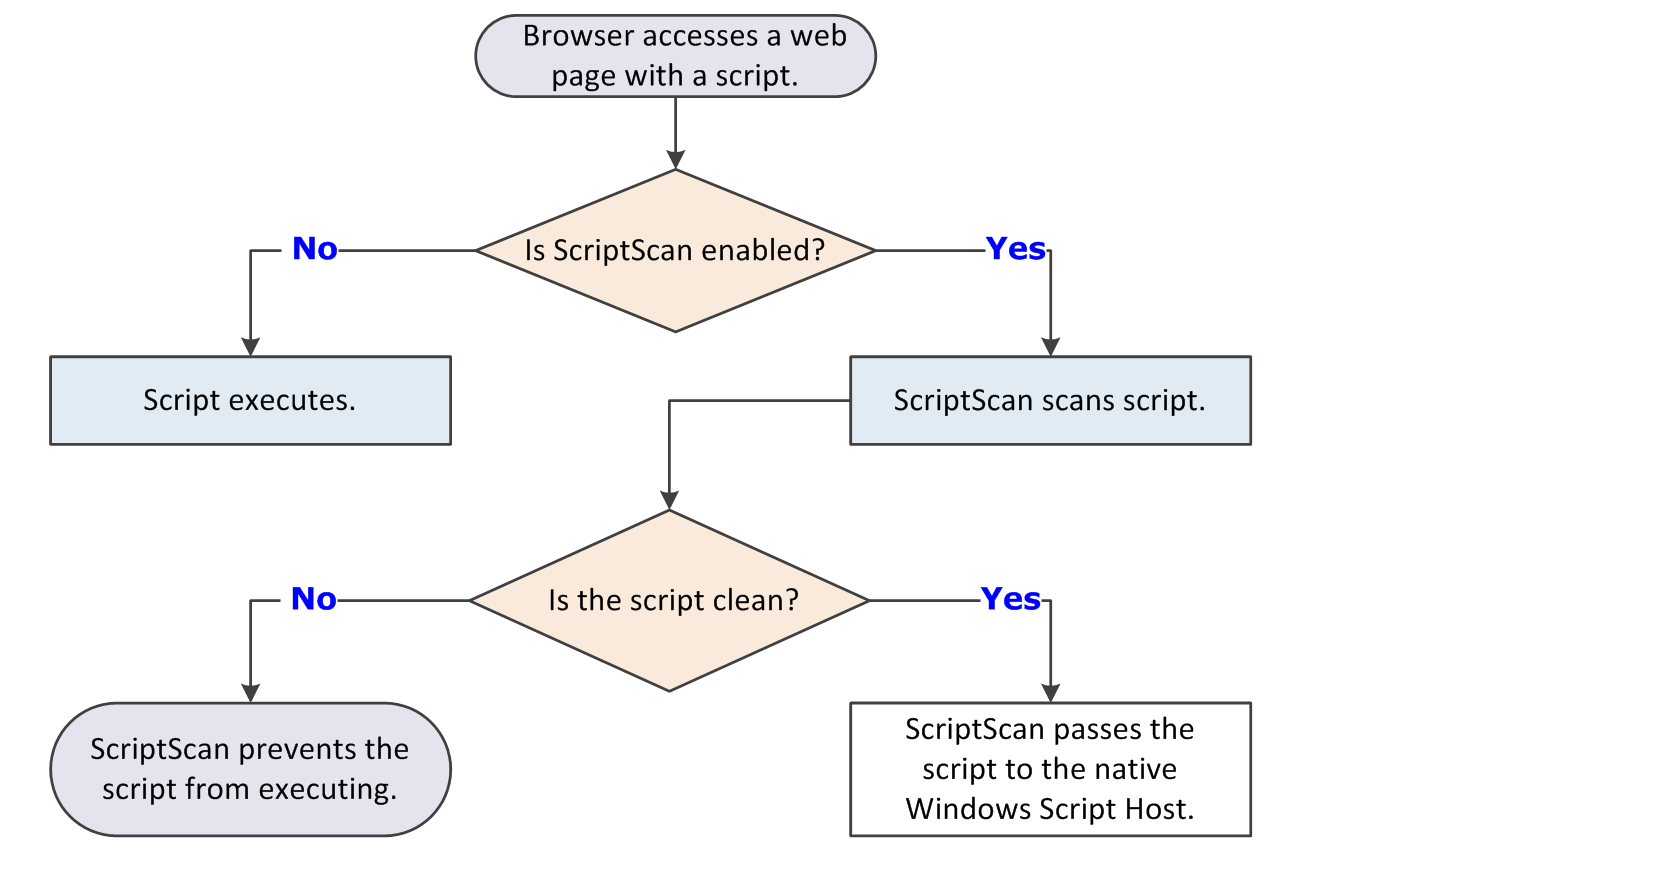
If the script is clean, the script scanner passes the script to the native Windows Script Host.
If the script contains a potential threat, the script scanner prevents the script from executing.
Best practices: ScriptScan exclusions
Script-intensive websites and web-based applications might experience poor performance when ScriptScan is enabled. Instead of disabling ScriptScan, we recommend specifying URL exclusions for trusted sites, such as sites in an intranet or web applications that are known safe.
You can specify substrings or partial URLs for ScriptScan exclusions. If an exclusion string matches any part of the URL, the URL is excluded. For example, specifying an exclusion of "msn.com" excludes both http://money.msn.com and http://www.msn.com.
When creating URL exclusions:
Wildcard characters aren't supported.
More complete URLs result in improved performance.
Don't include port numbers.
Use only fully qualified domain names (FQDN) and NetBIOS names.
Note
New URL exclusions are not applied to currently running Internet Explorer browsers. You must restart Internet Explorer for the new exclusions to take effect.