The Trellix SIEM (Security Incident/Event Management) solution monitors networks and helps you identify vulnerabilities and threats. The solution is made up of hardware appliances, virtual devices, and the Trellix ESM application. A Trellix ESM, a receiver, and Trellix Enterprise Security Manager are required. Other devices are optional.
Trellix ESM components include:
Trellix Enterprise Security Manager — The core device of the Trellix SIEM solution and the primary device on which an analyst identifies vulnerabilities and hunts threats. It is also where administrators configure the system, including data sources, alarms, rules, and so on. The Trellix ESM holds events and flows collected by receivers (SIEM Collectors).
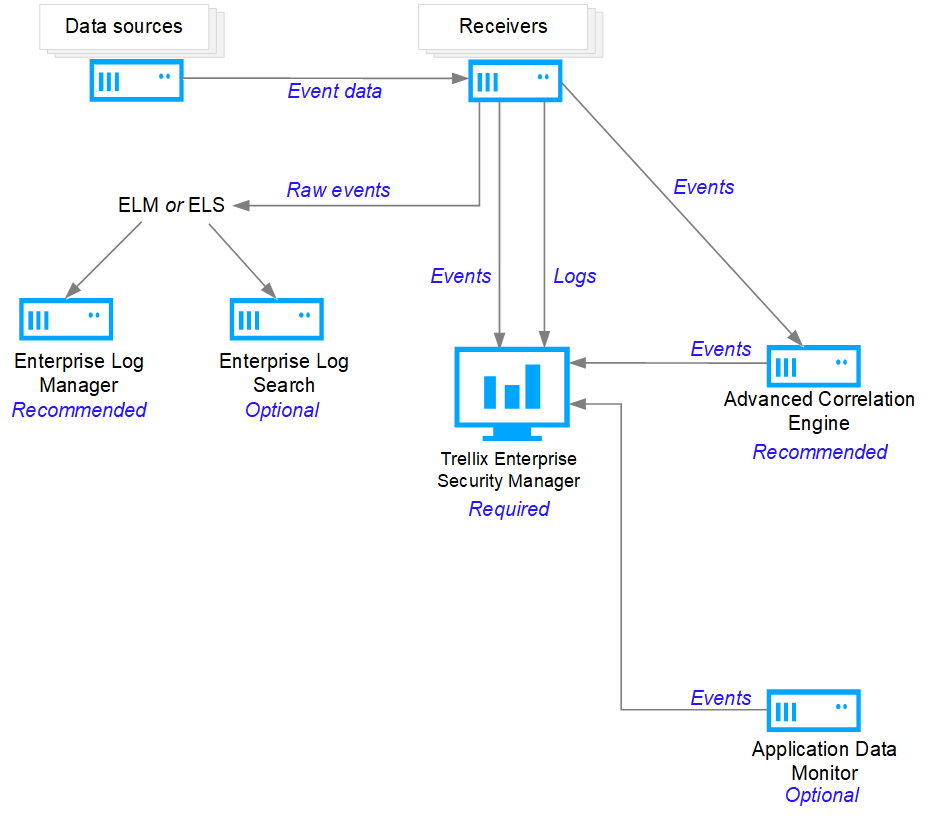
Trellix Enterprise Security Manager - Event Receiver Component (Trellix ESM - ERC) — Available as a hardware component or VM software installation, it collects 3rd party logs, events, and flow data for correlation and analysis by an Trellix ESM device.
Trellix Enterprise Security Manager - Enterprise Log Manager (Trellix ESM - ELM) — Available as a hardware component or VM installation, it provides compliant log management functions. Requires a Trellix ESM device and SIEM Collector. Trellix ESM - ELM can be thought of as "cool" storage. It hashes for forensic integrity and compresses for storage efficiency (in a small 2U package). It can be searched, but only in rare instances. And it should be the storage of record which allows for full log retention.
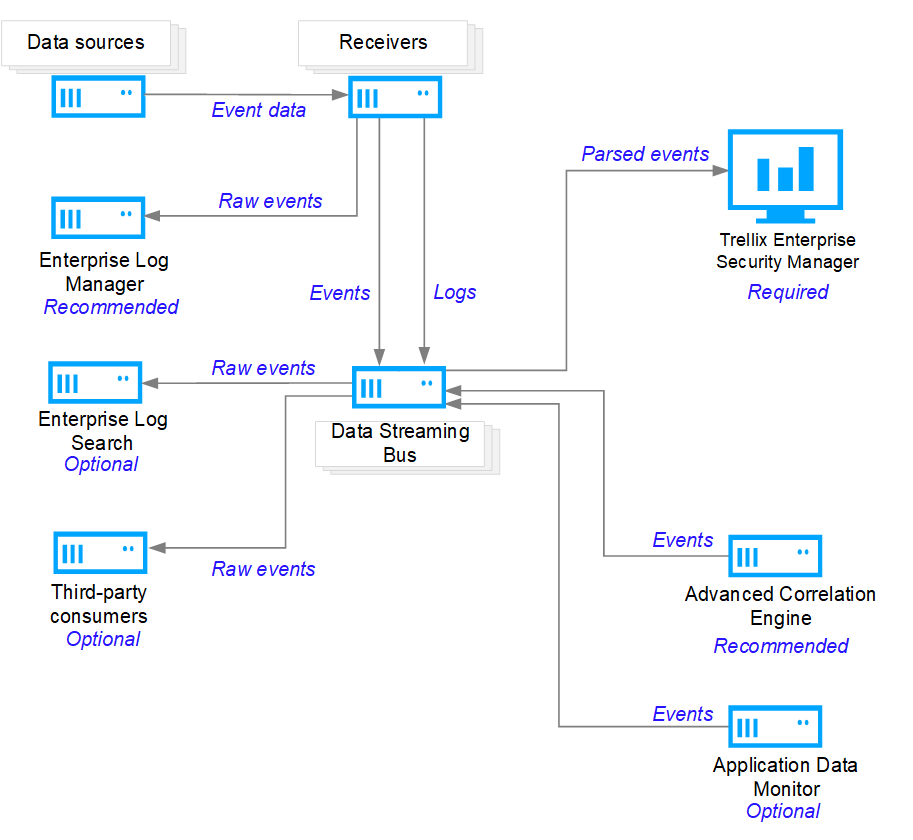
Trellix Data Streaming Bus - Facilitates device interconnection and reliability and provides a streaming data platform for external integrations. Trellix DSB is built on clustering technology that allows you to horizontally scale to improve retention and performance while also increasing reliability by adding fault tolerance and data replication.
Trellix Enterprise Security Manager - Enterprise Log Search(Trellix ESM - ELS) — Stores raw logs collected from your network for longer storage than an Trellix ESM and faster searching than an Trellix ESM - ELM. The SIEM Collector device collects logs from your network devices, parses them to create events, and can send the raw unparsed log to the Trellix ESM - ELS for long-term storage with faster search capability. Comparing an Trellix ESM - ELS to an Trellix ESM - ELM, the Trellix ESM - ELS has a faster search but less storage capacity than the Trellix ESM - ELM.
Comparing an Trellix ESM - ELS to an Trellix ESM, the Trellix ESM - ELS stores unparsed events and the Trellix ESM stores parsed events. The Trellix ESM - ELS has greater storage capacity but slower search than the Trellix ESM.
Trellix Enterprise Security Manager - Advanced Correlation Engine (Trellix ESM - ACE) — Enhances alarms and notifications by detecting risks across many events and flows that an Analyst would otherwise have to hunt and track individually. The Trellix ESM - ACE improves risk detection through rule-less risk detection. Rule-based processing can also be shifted from Receivers to an Trellix ESM - ACE so that more data can be analyzed without overloading Receivers.
Trellix Enterprise Security Manager - Application Data Monitor — A hardware or VM component that monitors more than 500 known applications through the entire layer stack and captures full session detail of all violations.
Trellix Direct Attached Storage (Trellix DAS) — A hardware component connected to the Trellix ESM, Trellix ESM - ELM, or Trellix ESM - ELS to expand storage space.
Note
In redundant solutions, one Trellix DAS device is required in each system. For example, two redundant Trellix ESM - ELMs require two Trellix DAS devices.
System diagram without a Trellix Data Streaming Bus
 |
System diagram with a Trellix Data Streaming Bus
 |