The Threat Prevention module protects your Mac from malware proactively with the predefined actions upon detecting malware and suspicious items.
When enabled, Threat Prevention checks for viruses, trojans, unwanted programs, and other threats by scanning items. The software scans files and folders on local, network-mounted volumes, and removable media whenever you create or access them. You can also run scans on demand.
The software uses the latest anti-malware engine that:
Performs complex analysis using the malware definition files (DAT).
Decodes the contents of the item you access.
Compares them with the known signatures stored in the DAT files to identify malware.
In addition, Trellix® Global Threat Intelligence (heuristic network check for suspicious files) looks for suspicious files and programs running on client systems that Threat Prevention protects.
Note
The system must have Internet connection to access Trellix GTI.
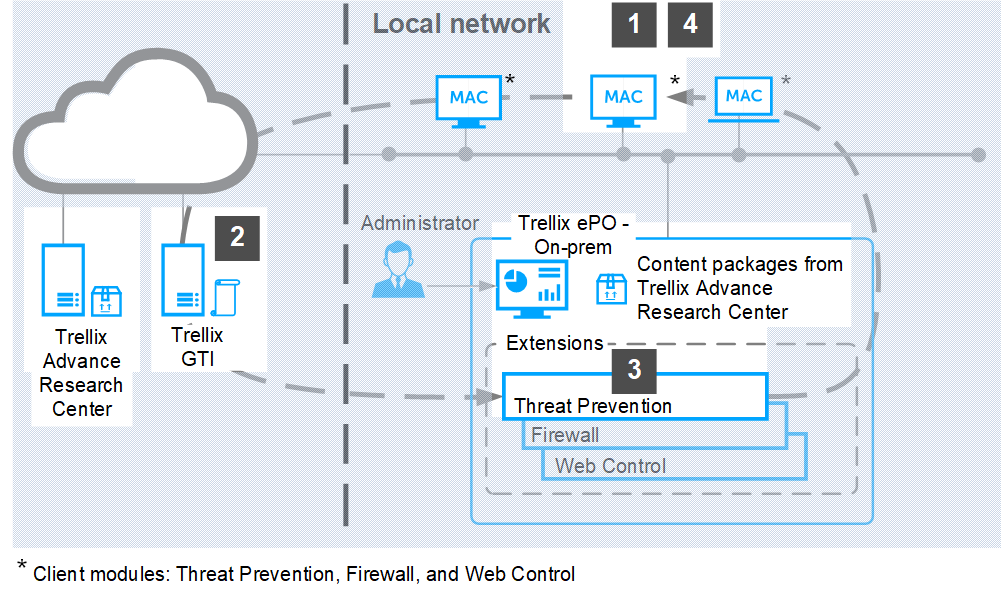
The high level work flow of Threat Prevention protection is:
Mac endpoints are protected by Threat Prevention in your network with Trellix GTI enabled.
Trellix GTI queries and DAT scans determine whether the file is malicious.
Threat Prevention analyzes the file rating and checks for the action configured in the policy.
Threat Prevention takes action on the file according to the configuration.
This diagram illustrates the workflow of Threat Prevention module.