When the module is installed and enabled on an endpoint, it monitors the event activity for that endpoint and determines if any event matches a defined rule. If a rule match is determined, information about the event, rule, and additional metadata is forwarded to Helix for collection. Within Helix, you can search the data collected or configure rules to further monitor the incoming hits in order to trigger an alert.
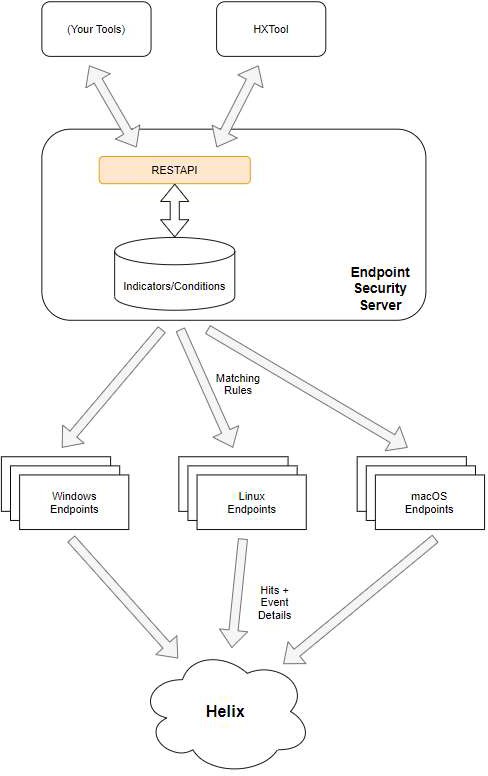
The endpoints receive their rule definitions from the Endpoint Security Server and are kept in sync with any modifications made to those rules. The pre-configured rules are all enabled by default. However, you can disable them if you find they are not appropriate for your needs.
You can create custom rules to monitor events according to your needs. The HXTool on the FireEye Market provides the ability to create and manage rules through the user interface. The module also comes with rich API with which you can connect your own tools to perform management and maintenance.
The rules created are similar in structure and capability to match activity events, as rules for alerting IOCs. Custom rules are defined using the IOC 1.1 format and can leverage existing rule definitions.
The module also keeps track of the volume of hit data produced by each endpoint, as well as an aggregated total across all endpoints. This can guide you towards tuning the rules according to your data volume constraints.