The Host Filtering tab is the primary mechanism to improve server module performance (namely, the UI query responsiveness). It consists of features to purge existing data and to filter (drop) future events received from endpoints.
Filtering source or target hosts
One technique to reduce the volume of events in the database is to identify systems responsible for the highest volume of events. The top section of the Host Filtering tab provides three columns to achieve this:
Sources: Systems where the highest volume of logon activity originates from
Targets: Systems where the highest volume of logon activity is destined for (often domain controllers)
Filtered: Source or target systems that were purged from the database, and are now being filtered
Click a source or target system will move the system to the Filtered column. Likewise, clicking on systems in the Filtered column will remove them from filtering. Click Save to remove existing events for the filtered systems and drop all future events. Note that events are only removed where the source system is the logon source and the target system is the logon target.
The figure below shows filtering enabled for two source systems and two target systems.
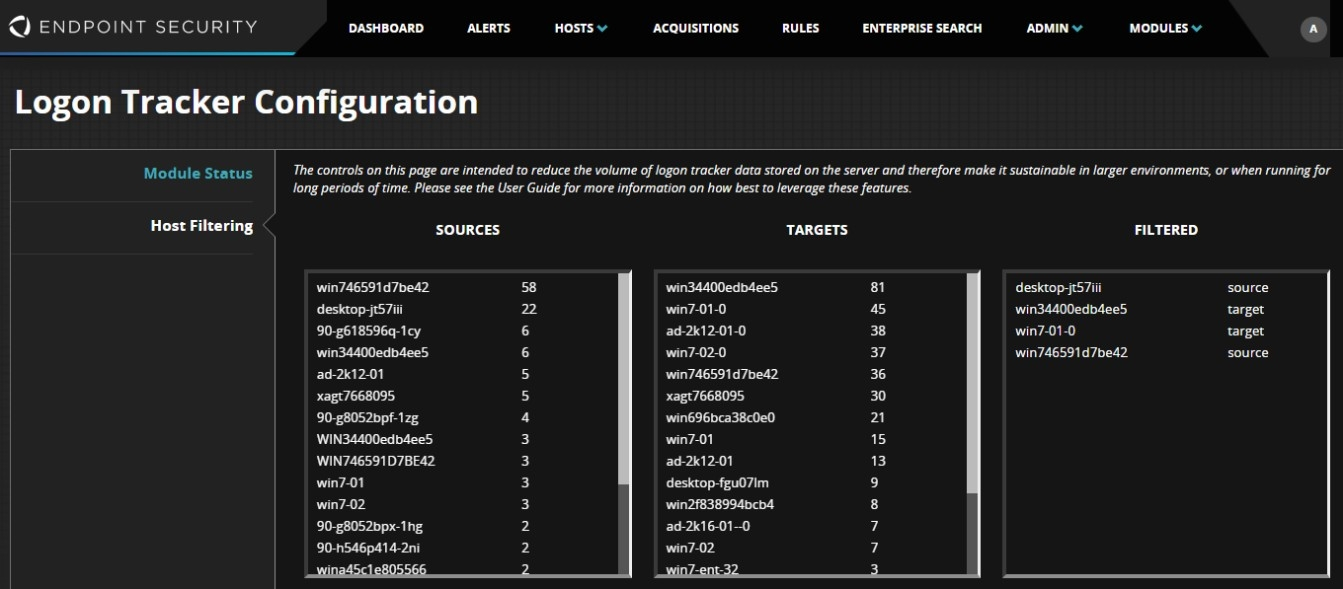
Filtering settings
In addition to filtering specific source or target hosts, additional settings are available at the bottom of the Host Filtering page. These settings can be used to filter old events, duplicate events, and remote computer account logons.
Event Age Limit (days): Filter events where the logon time is older than the specified number of days (0 is unfiltered). For example, a value of 30 means that only logon activity that occurred in the past 30 days will be stored. This is a critical setting for a successful long-term deployment of Logon Tracker.
Duplicate Event Limit: Filter duplicate events that have occurred greater than the specified limit (0 is unfiltered). Typically, repetitive events are not interesting in the context of investigating lateral movement. The recommended setting is 100. Events are considered duplicate when the same source account/system connects to the same target account/system using the same protocol.
Drop Remote Computer Account Logons: Filter events if they originate from remote computer accounts. Remote computer accounts are identified by the source hostname followed by a $. For example, logon activity into server DC-01 using account WKST01$ would be filtered if it originated from workstation WKST01.
It is recommended that any host filtering changes discussed in this section be complemented with adjustments to agent policy, and even reverted once policy changes are in place. For example, place hosts with high volumes of logon activity such as domain controllers, file servers, and web servers into their own policies. Configure these policies with more conservative logon tracker settings such as increased cache timeout, no backfill, no network events, and so on. After the policy has been updated, filtering of source and target systems is removed. This approach would enable detecting interesting logons such as RDP activity into a domain controller that would otherwise be lost with host filtering.