ATP and Threat Prevention provide technologies that protect against fileless attack methods in which no persistent malware file exists. Fileless attacks include network streaming of payloads and commands, abuse of dual-use applications, and live-off-the-land techniques.
Protection against fileless attack methods requires security around behaviors and activities instead of files and objects. Trellix ENS technologies offer layered security that enables you to catch fileless attacks at multiple points in the attack chain.
Detect malicious behaviors and activities with attack behavior blocking rules
ATP identifies fileless threats by observing suspicious behaviors and activities and blocking those activities. When ATP determines that the context of an execution is malicious, it blocks the malicious activity, and if necessary, remediates.
A set of ATP attack behavior blocking rules determines what processes can and can't do within a specific context to protect against fileless attack methods. For example, Microsoft Office applications generally aren't allowed to start script interpreting programs such as PowerShell and WScript because that's not a context in which IT administrators would start those types of programs.
Trellix releases new ATP rules in AMCore content. For information about the latest ATP content, see the Trellix TIE and ATP Security Content Release Notes.
For information about ATP rules, including rule IDs and their corresponding rule names and descriptions, see KB82925.
Scan obfuscated scripts
The ML Protect scanner inspects suspicious activities on client systems and uses machine-learning techniques to detect malicious patterns. The ML Protect scanner can scan a network-streamed script, determine if it's malicious, and if necessary, stop the script.
ML Protect script scanning integrates with AMSI to protect against non-browser-based scripts, such as PowerShell, JavaScript, and VBScript.
Visualize fileless threat detections
The Story Graph in the Threat Event Log provides a visual representation of fileless threat detections. You can examine the context of threats by reviewing the details of events leading up to a detection. The Story Graph helps you to identify what was executed, why ATP thinks it's malicious, where it came from, and where in the attack chain ATP stopped the threat.
Fileless attack example
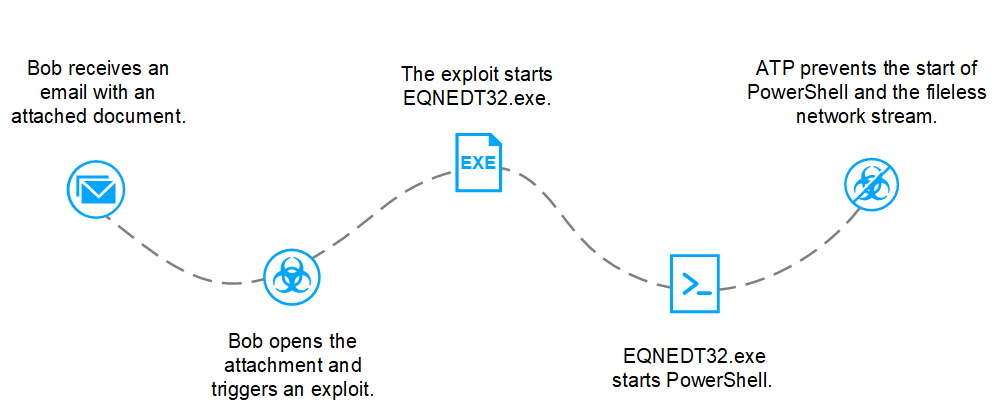
Here's an example of a fileless attack:
Bob (user) receives a Microsoft Word document as an email attachment.
Bob opens the attachment and the malicious content triggers an exploit.
The exploit starts the Microsoft Equation Editor (EQNEDT32.exe).
EQNEDT32.exe uses the Command Prompt to start PowerShell to network stream payloads and commands to PowerShell.
ATP detects that EQNEDT32.exe starting PowerShell is not a normal activity and prevents the start of PowerShell. ATP stops the attack before the fileless network stream can start.
Trellix delivers updates to fileless protection technologies in AMCore content updates.