Adaptive Threat Protection uses an application's reputation to determine whether Dynamic Application Containment runs the application with restrictions. Dynamic Application Containment blocks or logs unsafe actions of the application, based on containment rules.
As applications trigger containment block rules, Dynamic Application Containment uses this information to contribute to the overall reputation of contained applications.
Other technologies, such as Trellix® Active Response, can request containment. If multiple technologies registered with Dynamic Application Containment request to contain an application, each request is cumulative. The application remains contained until all technologies release it. If a technology that has requested containment is disabled or removed, Dynamic Application Containment releases those applications.
Dynamic Application Containment workflow
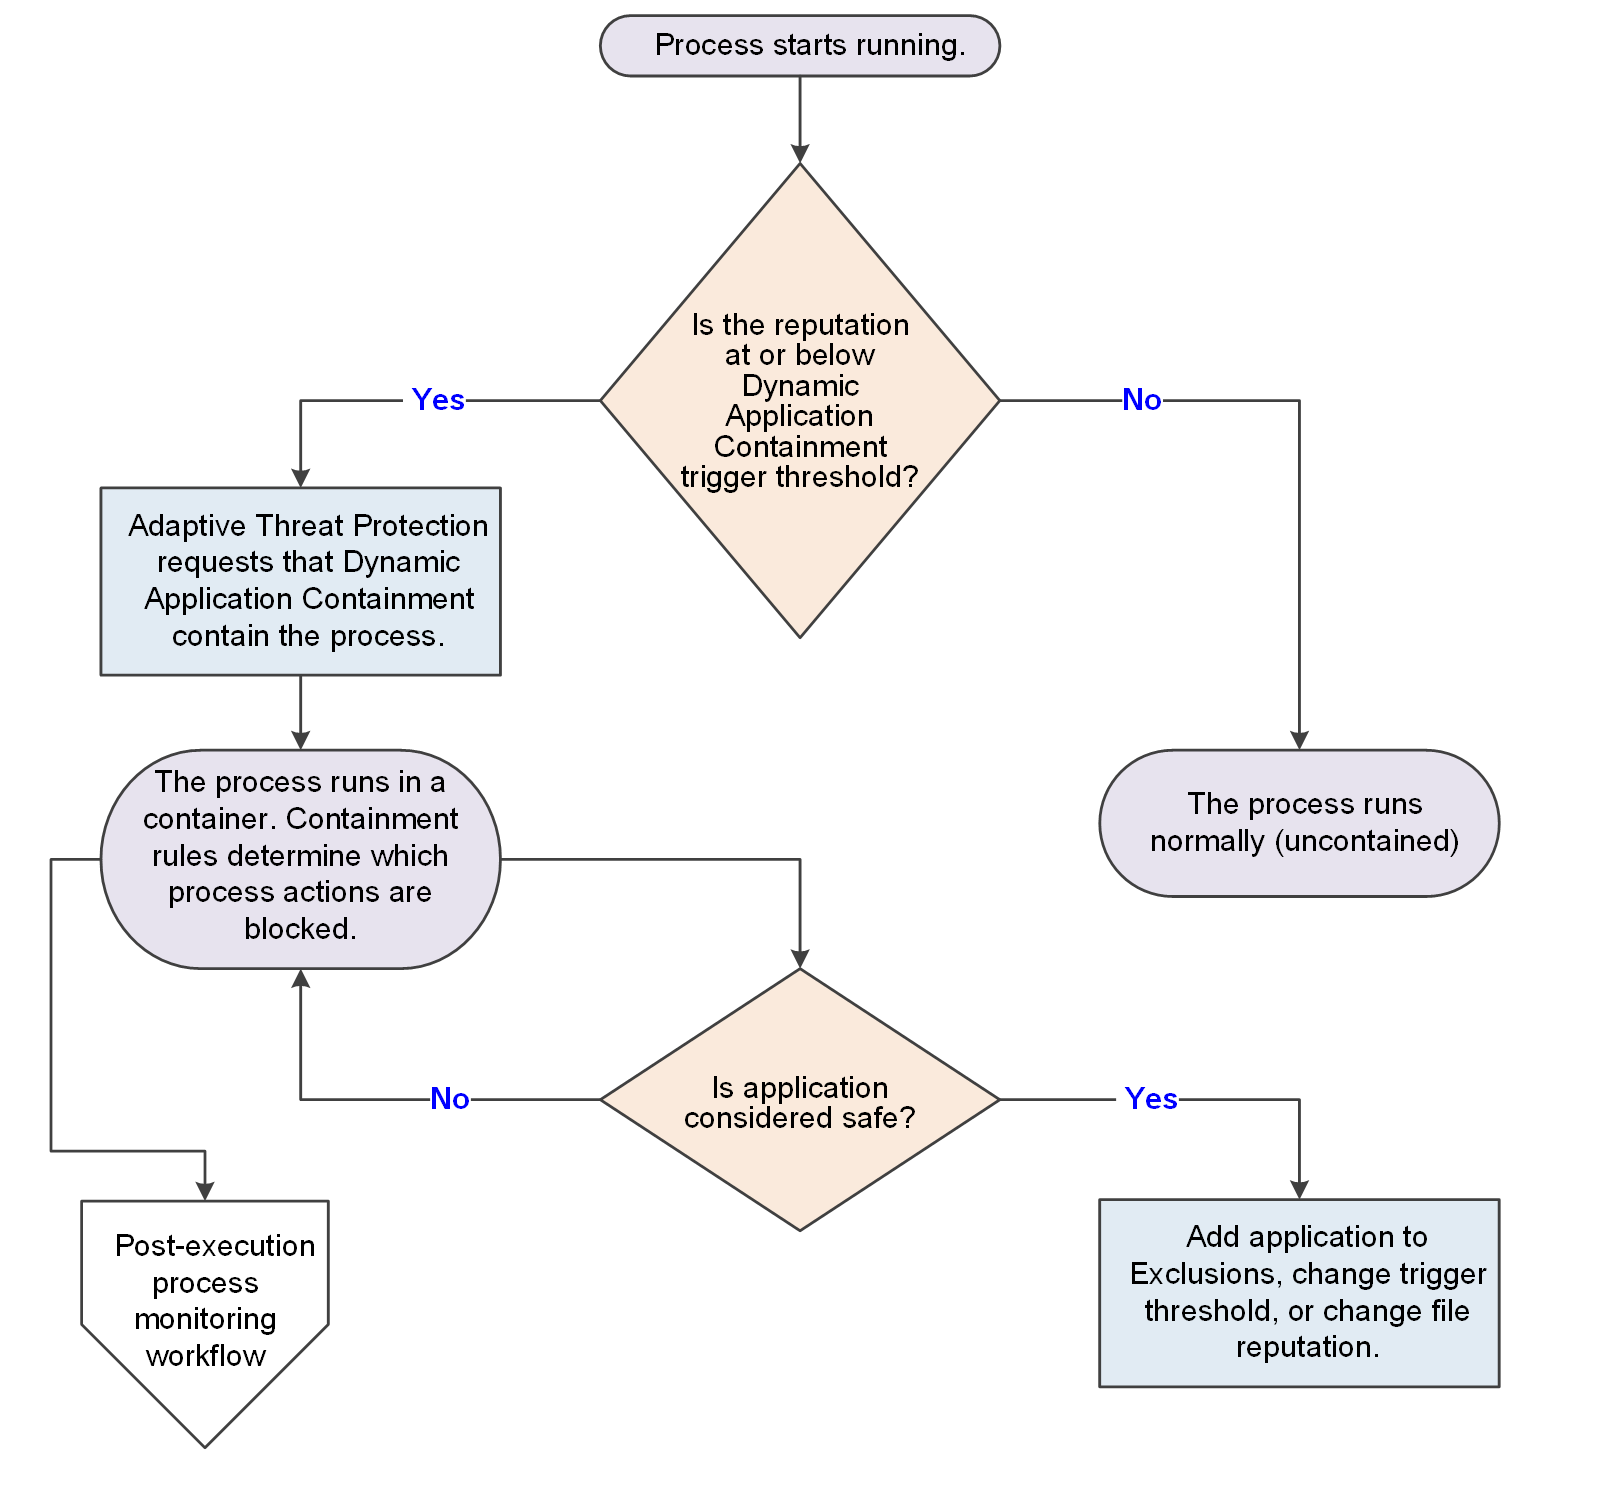
The process starts running.
If the reputation for the process, or a DLL dynamically loaded into the process, is at or below the containment reputation threshold, ATP notifies Dynamic Application Containment that the process has started and requests containment.
If a DLL with a reputation at or below the containment threshold is dynamically loaded into the process ATP requests containment for the process, regardless of the process reputation.
Dynamic Application Containment contains the process.
If configured, Dynamic Application Containment updates the Event Log in the Trellix Endpoint Security (ENS) Client and sends an event to ePO - On-prem, if applicable, to notify when:
An application has been contained.
A contained application attempts to violate the containment rules.
You can view Dynamic Application Containment events in the Threat Event Log in ePO - On-prem.
If the contained application is considered safe, you can allow it to run normally (not contained).